Beginner Steps. Advanced AI.
Published guideUpdated
Chapter 2 of 20Set up
Create your GitHub project
Create a free GitHub account and a private home for your website files.
Let's give your website a safe place on GitHub.
Follow the pictures
Illustrated examples. Your app may look different. Tap an image to enlarge it.
-
Create your account
Create a GitHub Free account. Choose a username and verify your email.
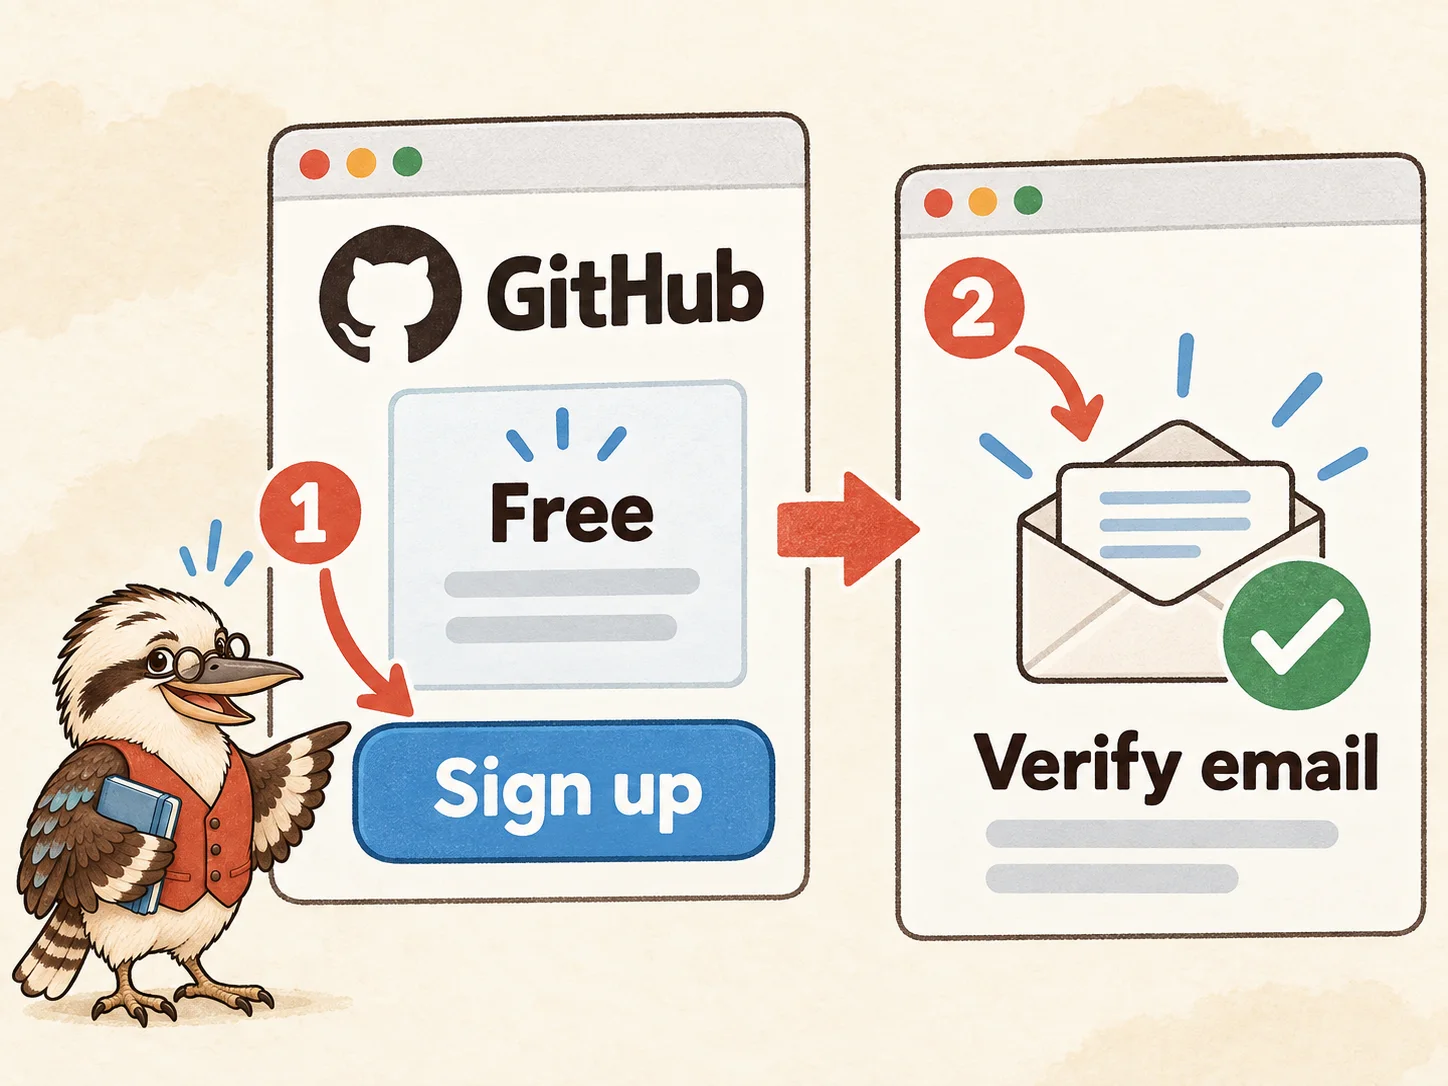
Illustrated example - Click path
- GitHub → Sign up → Verify email
Look for: Your GitHub account opens and your email is verified.
More help with this action
GitHub is separate from OpenAI. GitHub Free supports private repositories, so no paid subscription is needed here. Advanced features and hosting services have their own plans. A repository stores project files and history. Private visibility limits source access; it does not secure the website or stop hosting from publishing it later. Never store credentials in repositories.
Show the steps
- Follow the GitHub account creation guide, choose a username, finish registration, and verify your email.
- Use an email address you can access. Choose the Free personal plan if GitHub offers a choice.
- Open the verification email and follow its instructions; check spam if it does not arrive.
You should now see: Your GitHub account opens and your email is verified.
-
Protect your sign-in
In GitHub, open Settings → Password and authentication. Set up two-factor authentication with an authenticator app.
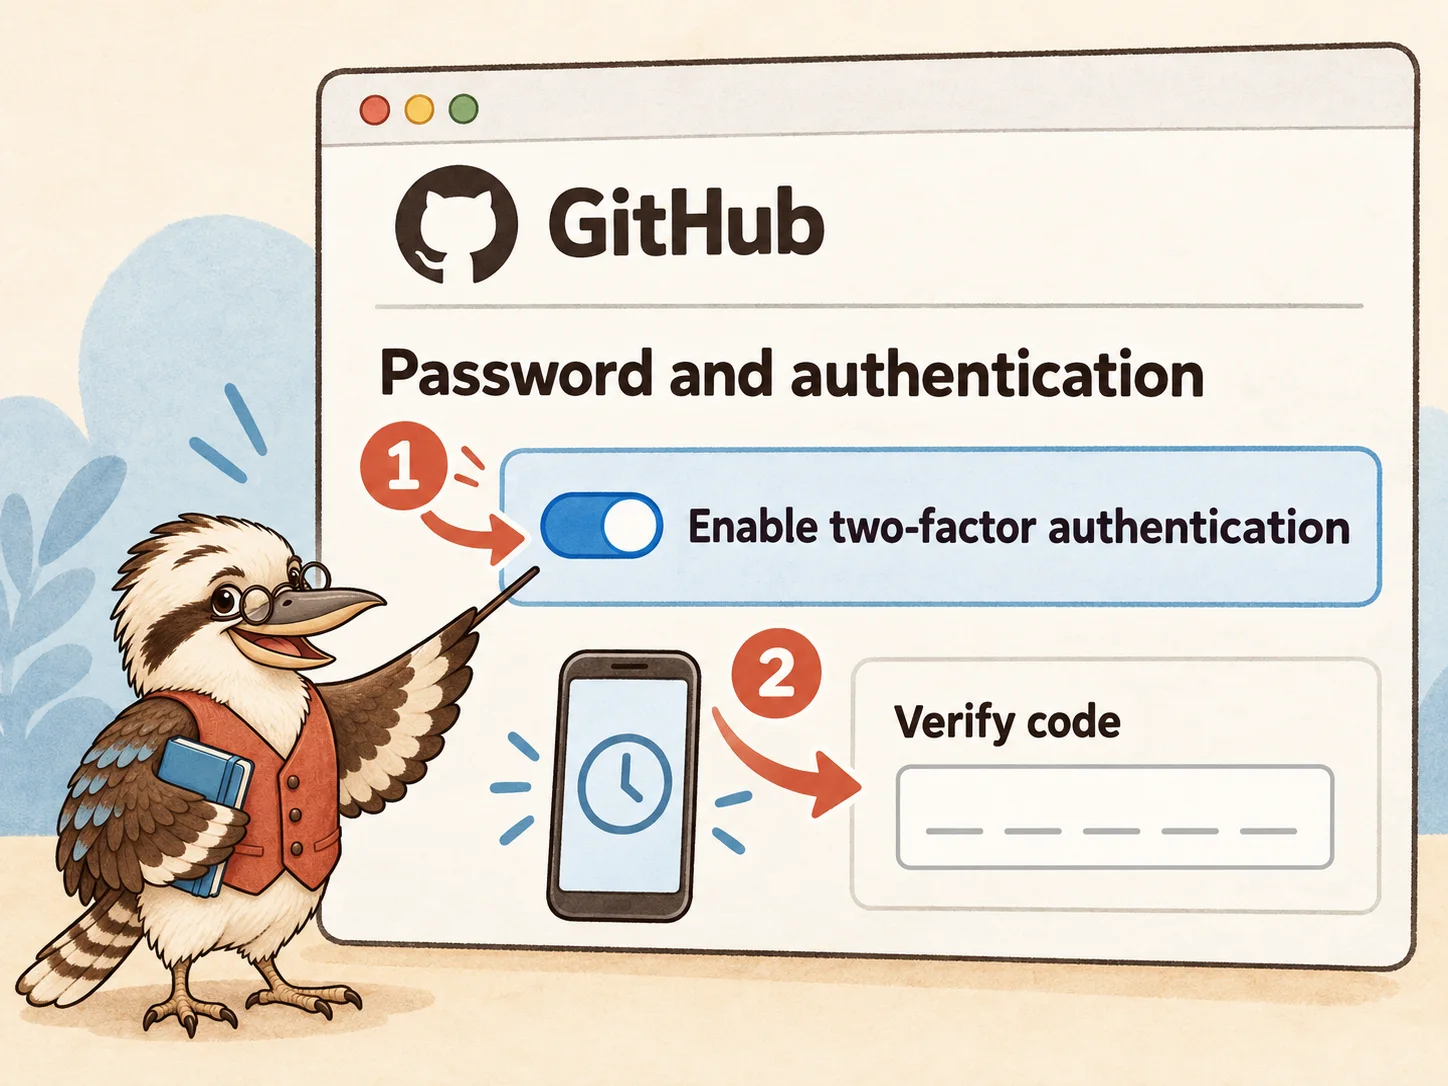
Illustrated example - Click path
- Profile picture → Settings → Password and authentication → Enable two-factor authentication
Look for: Your authenticator app is linked; finish by saving recovery codes in the next action.
More help with this action
Follow these steps if you want more help.
Show the steps
- Open your profile picture > Settings > Password and authentication. Enable two-factor authentication using an authenticator app and complete verification.
- Use an authenticator app you trust on your phone or computer.
- Follow GitHub's scan or setup-key instructions inside your own account, then enter the app's temporary code.
- Keep the setup secret and codes private. Continue to the recovery-code screen; the next action completes setup.
You should now see: Your authenticator app is linked; finish by saving recovery codes in the next action.
-
Save your backup codes
Save your recovery codes in a password manager. Confirm you can find them, then finish setup.
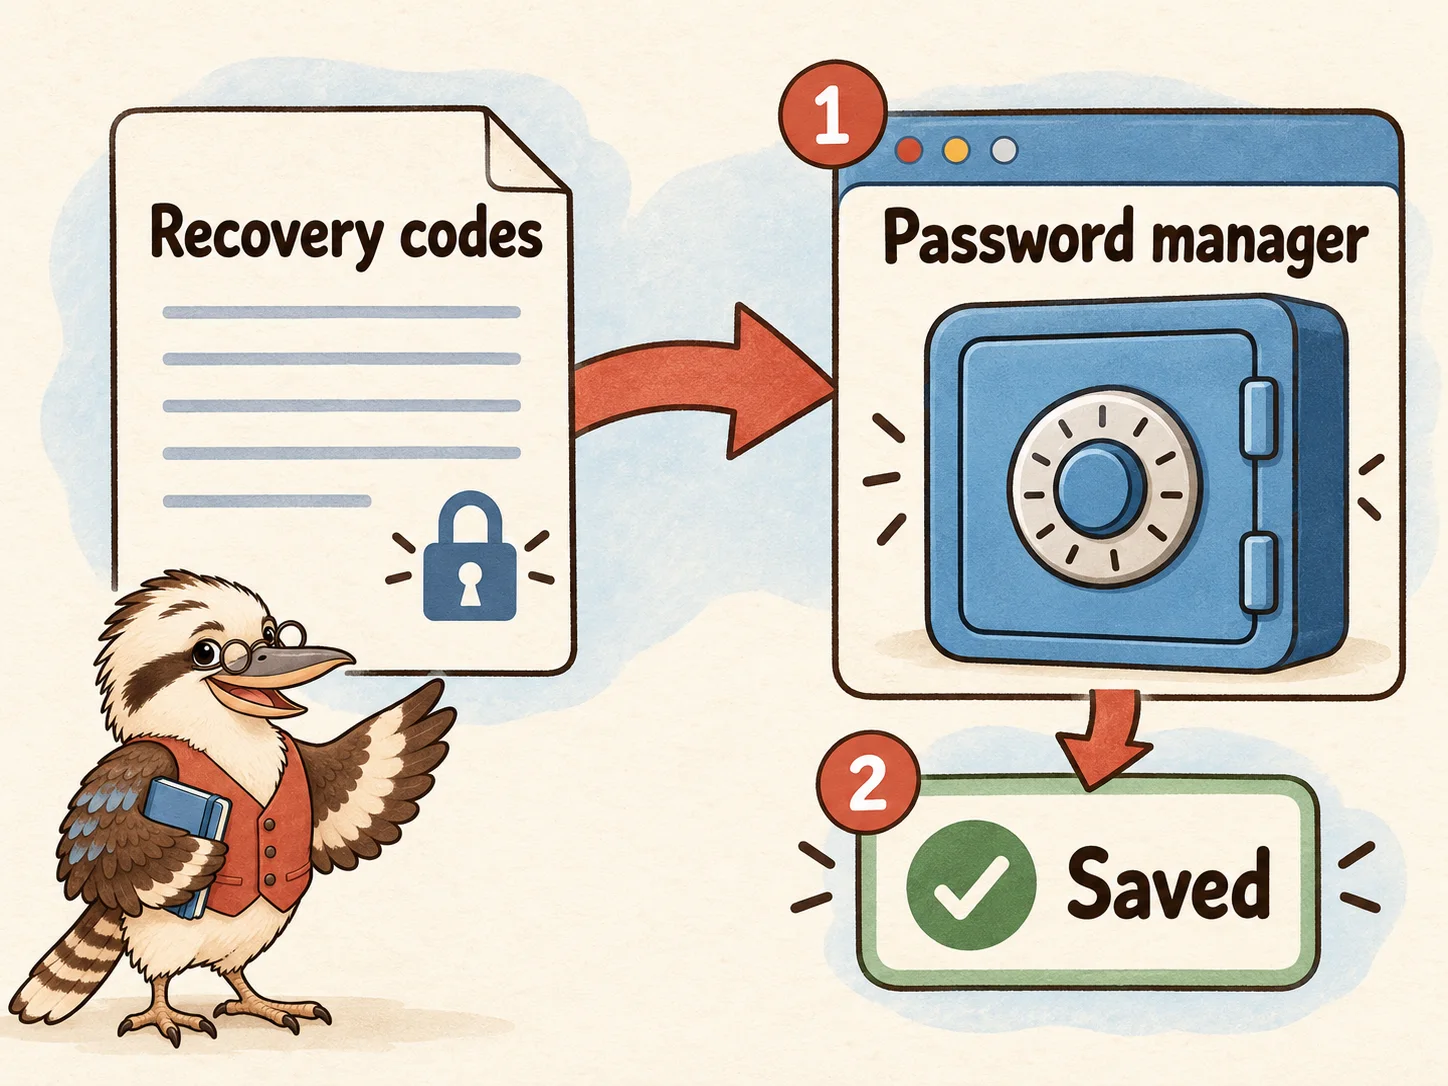
Illustrated example - Click path
- Save recovery codes → Password manager → Confirm saved
Look for: Two-factor authentication is enabled and you can find your recovery codes.
More help with this action
Follow these steps if you want more help.
Show the steps
- Save your GitHub recovery codes in a password manager or another protected location independent of your phone. Confirm you can find them.
- On the Save your recovery codes screen, download or copy the codes into protected storage.
- Check that you can open the saved item independently of your authenticator device. Avoid leaving an unprotected copy in Downloads.
- Back on GitHub, choose I have saved my recovery codes to finish enabling two-factor authentication.
You should now see: Two-factor authentication is enabled and you can find your recovery codes.
-
Prepare your repository
Choose GitHub’s plus menu → New repository. Name it fieldnotes-studio, choose Private, and turn Add README on.
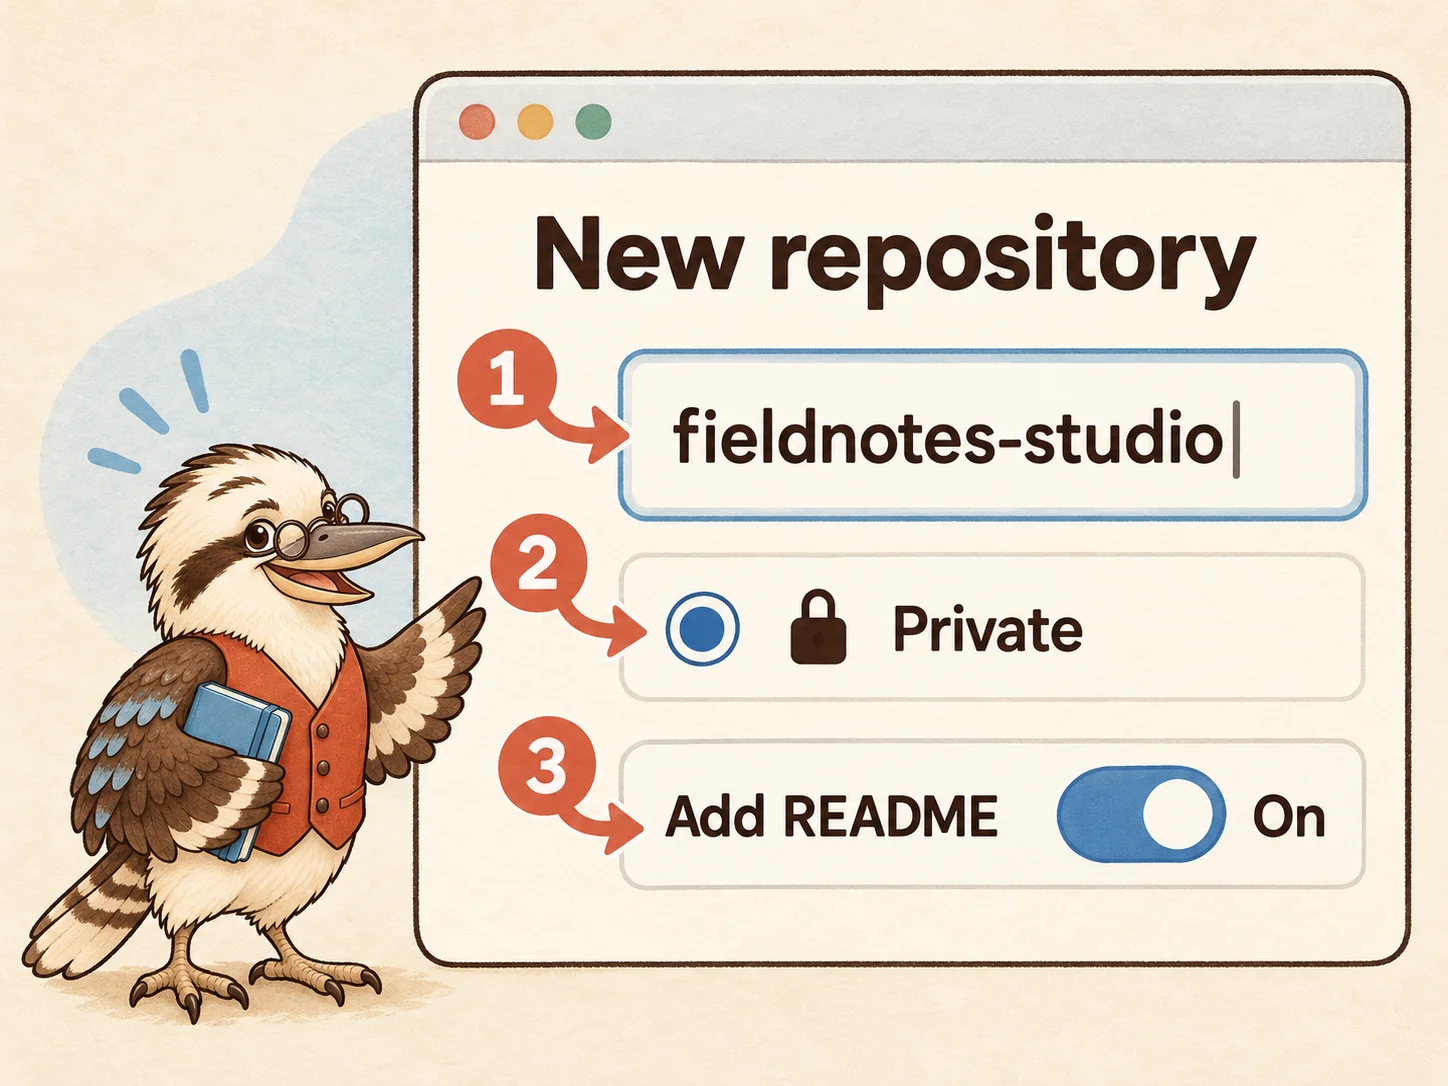
Illustrated example - Click path
- Plus menu → New repository
- Choose
- fieldnotes-studio → Private → Add README: On
Look for: The form shows fieldnotes-studio, Private, and Add README turned on.
More help with this action
Follow these steps if you want more help.
Show the steps
- Use GitHub's plus menu > New repository, following the repository creation instructions. Name it fieldnotes-studio, choose Private, and enable Add README.
- Choose your own account as the repository owner.
- Use the exact name fieldnotes-studio so later commands match. Review the form before creating it.
You should now see: The form shows fieldnotes-studio, Private, and Add README turned on.
-
Create and bookmark it
Click Create repository. Bookmark its page; chapter 3 uses your-username/fieldnotes-studio.
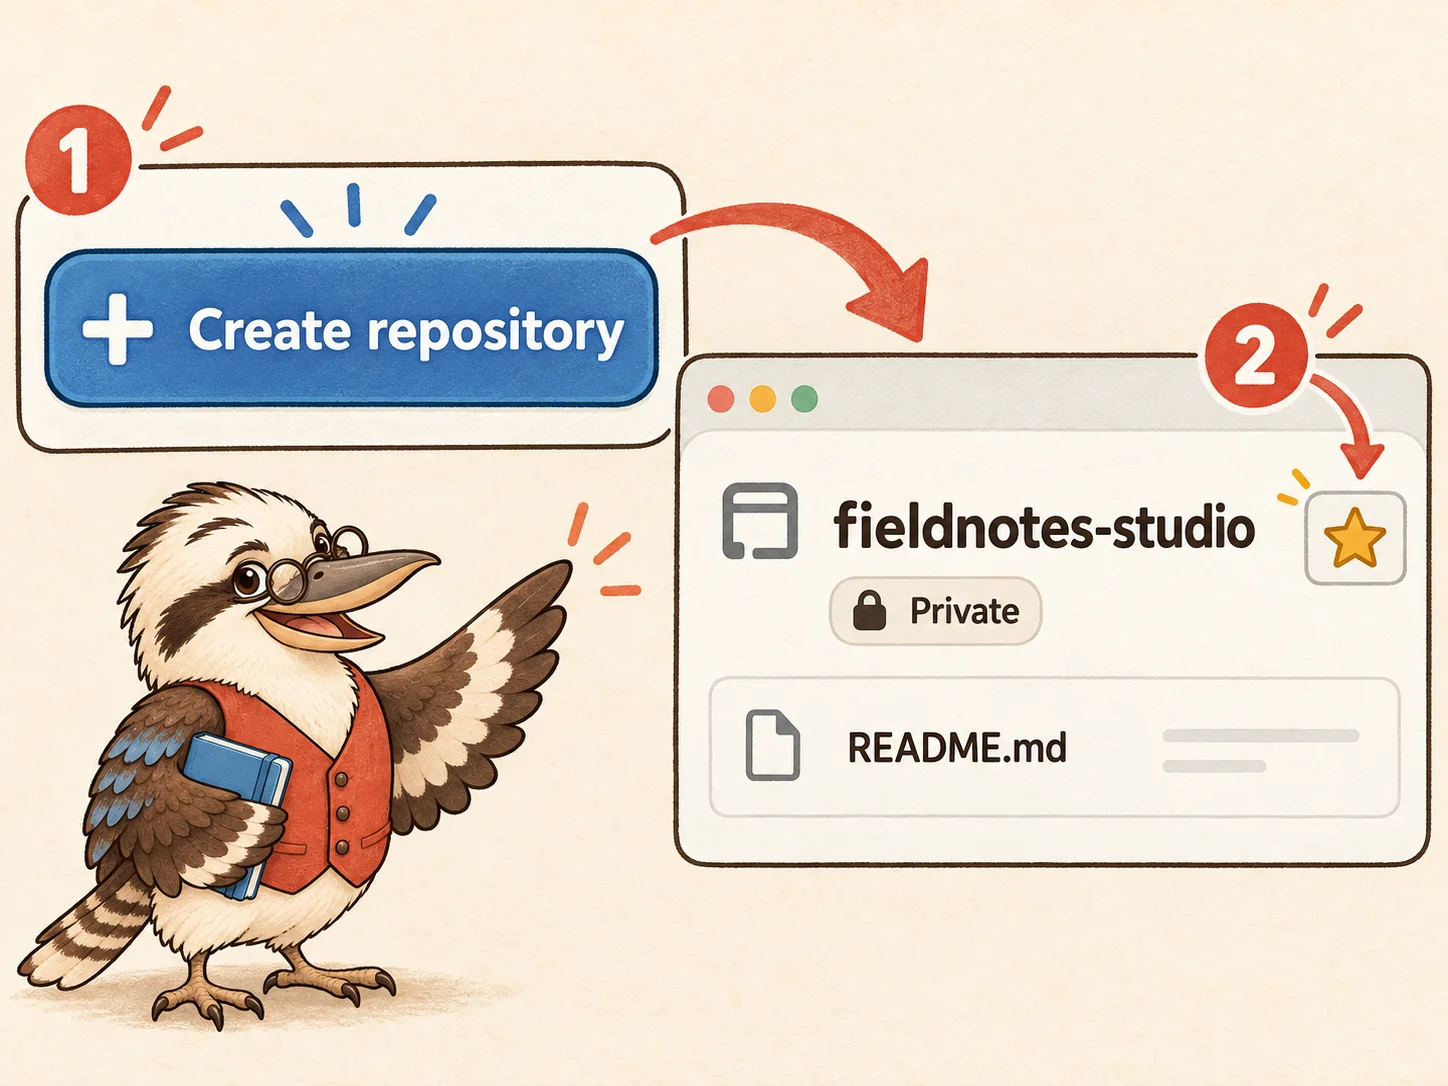
Illustrated example - Click path
- Create repository → Bookmark the page
Look for: The repository page shows fieldnotes-studio, Private, and README.md.
More help with this action
Follow these steps if you want more help.
Show the steps
- Create and bookmark the repository. The address ends in your-username/fieldnotes-studio; use that exact name when connecting the local project in chapter 3.
- Check the Private label and README.md on the new repository page.
- your-username is a placeholder for your real GitHub username. Note that owner/project part of the address.
- Creating a repository stores source files; it does not publish a website.
You should now see: The repository page shows fieldnotes-studio, Private, and README.md.
-
Save your first change
Open README.md → Edit. Add a short project description, then commit your first change and find it in the history.
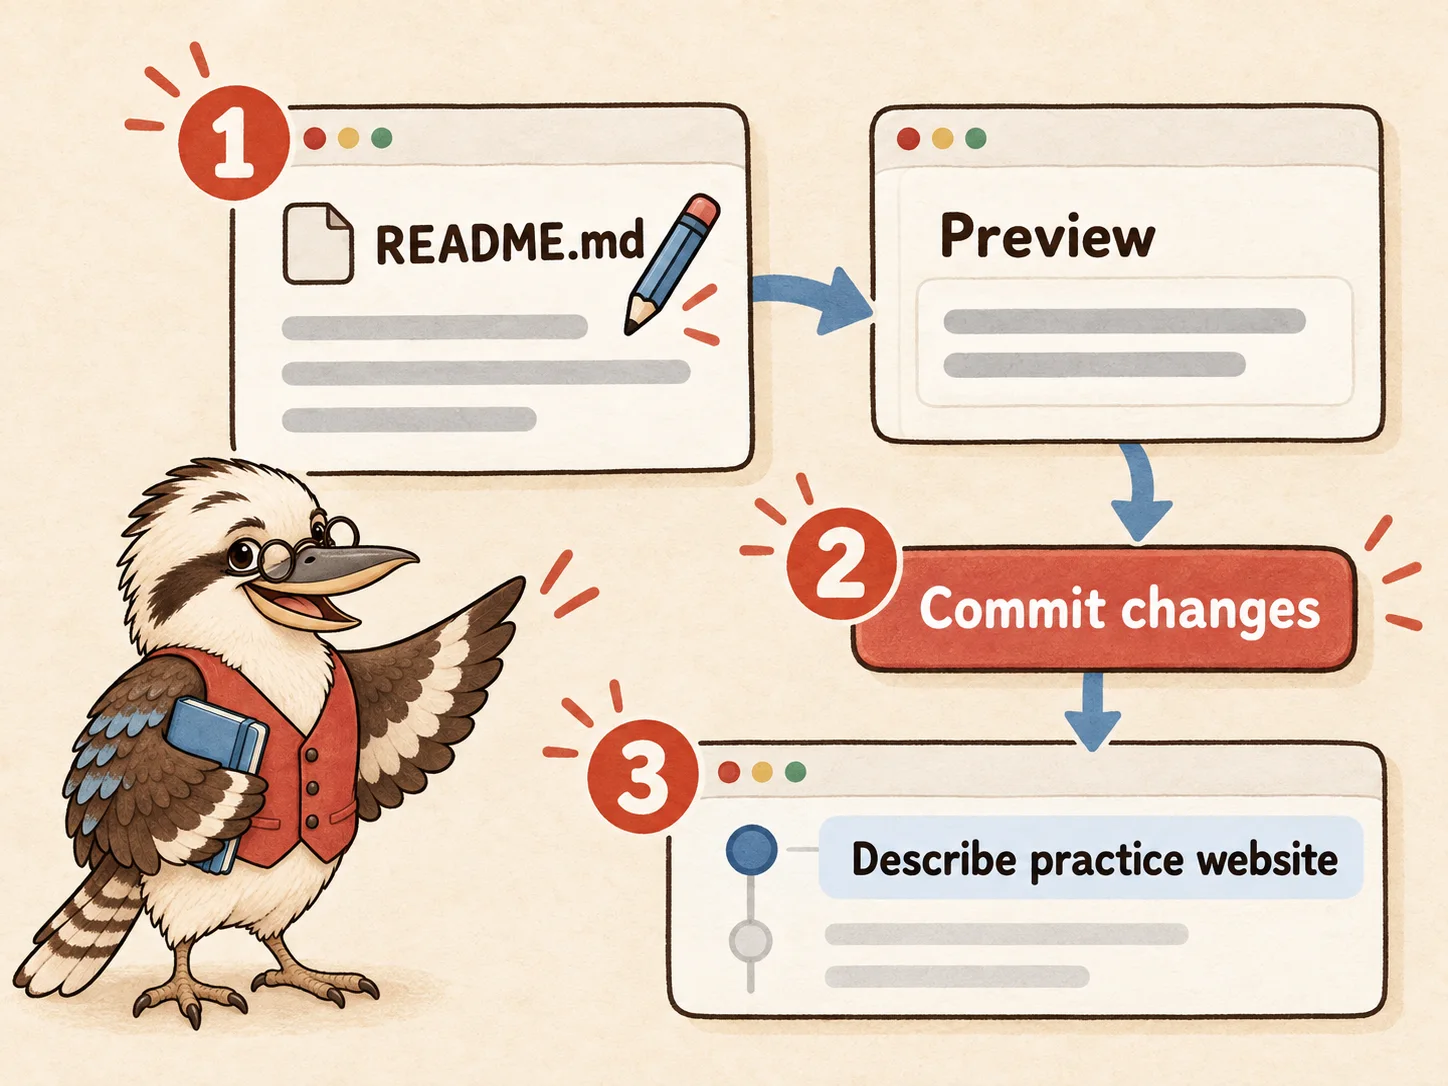
Illustrated example - Click path
- README.md → Pencil / Edit → Preview → Commit changes
- Message
- Describe practice website
Look for: GitHub history contains your README change and its commit message.
More help with this action
Follow these steps if you want more help.
Show the steps
- Follow GitHub's first-commit walkthrough: open README.md, choose Edit, and add a project description. Commit with the message Describe practice website, then find the history entry.
- Use a description such as: A four-page practice website for Fieldnotes Studio.
- Choose Preview and review the text before selecting Commit changes.
- For this new private practice project, save the small README edit to the current default branch. Chapter 3 creates a separate build branch.
You should now see: GitHub history contains your README change and its commit message.
Why this step matters
GitHub stores project files and their saved history. GitHub Free is enough for this private practice project.
Private limits access to the source. It does not make a published website private or keep passwords safe.
Basics, explained
Repository
A project folder together with a history of changes. GitHub stores repositories online; your computer will hold a local copy.
Commit
A named snapshot of selected project changes, with a message explaining what changed.
Two-factor authentication
A second sign-in check beyond your password, such as a temporary code from an authenticator app.
README
The introductory file explaining what a project is and how someone can work with it.
Ask your agent
PromptMake sense of GitHub
Explain a repository, a commit, and a local copy using a four-page website. I created a private repository called fieldnotes-studio with a README. Explain what I should see. Do not request credentials or recovery codes.If something goes wrong
- GitHub asks you to buy a plan.
- Choose the Free personal plan. This private practice repository does not require Pro.
- You cannot create the repository.
- Check email verification, including spam. Follow GitHub's verification help before creating another account.
Official links & further reading
Personal notes
Add questions, decisions or ideas for your website. Saved in this browser when available; export your notes to keep a copy. Never enter secrets.
Downloads & saved progressGuide, notes and personal checks
Download the complete guide or export your notes from every chapter. Instructions last reviewed: .
Checks and notes stay in this browser, separately for each language. Export your notes to preserve them. Never enter API keys or other secrets here.
NotesNotes as Markdown
Clipboard access is unavailable. Copy the visible, selected text below using your keyboard or browser menu.
0 of 65 checks marked across the guide
These are your saved personal checkmarks. They do not run tests or verify security, and are separate from the chapter position bar above.
Starter filesWorking instructions and four skills
These templates give your agent a starting set of working instructions. Review them, adapt them to your website, and save each file at the exact path shown, relative to your project folder.
A downloaded skill is an instruction file. It does not install a test runner, run a security scan, or prove your site is safe. The guide shows how to set up and check that work.
Download the instruction files in the language of this guide. Keep the technical filenames and paths as shown.
Download all starter filesFileAGENTS.md
# Website working agreements

This project follows the website brief and acceptance criteria we have agreed with its owner. Use the existing technology choices unless a concrete requirement calls for a change.

## How to work

- For a substantial feature, explain the proposed changes and verification plan before implementing it. Complete authorized local work in small, reviewable stages.
- Read the files relevant to the task. Keep unrelated pages and configuration intact.
- Explain new technical terms in plain language when reporting to the owner.
- Use the repository's website-design, clean-code, website-testing and website-security skills when their workflows apply.
- Record important decisions and unresolved content in the project's notes. Do not invent business facts, endorsements or publishing rights.

## Verification

- Inspect package.json to find the actual build, type-check and test commands. Do not invent a successful check or create a meaningless test just to make a command pass.
- Run checks appropriate to the change. Local tests use disposable fixtures and have no production access; run them and repair failures caused by the requested change without asking at every step.
- Verify visitor interactions in a browser when browser tools are available. Report checks that remain unavailable or incomplete.
- Show the owner a working local preview and summarise changed behaviour, evidence and remaining limitations.

## Credentials and publication

- Keep API keys and other secrets out of browser code, prompts, logs and Git. Store local secrets in ignored files or the chosen secret store.
- Local build and test work is authorized. Publishing the site, sending a real message, processing a payment or changing production data requires the owner's authorization for that action.
- Preserve a recoverable working version before release. Describe how to restore it.

These are starter agreements for a new tutorial project. Adapt them to the owner's actual requirements and existing authorization.
File.agents/skills/website-design/SKILL.md
---
name: website-design
description: Develop or refine a website's visual direction and responsive interface from its brief, content and existing design. Use for page design or visual implementation.
---

Read the website brief and any existing design notes relevant to the requested page. Work within the user's brand, content and technology choices.

When establishing a new direction, propose typography, a small colour palette, a spacing rhythm and a sample page. Explain how these choices support the audience and main visitor action. Use real content to judge hierarchy and line lengths.

Implement reusable elements for navigation, headings, buttons and repeated content. Give primary actions a clear visual hierarchy. Preserve visible keyboard focus, readable contrast and usable labels. Design narrow screens alongside desktop screens; check long headings, navigation and tap targets in a browser.

Use semantic HTML before adding custom interaction. Keep motion optional and respect reduced-motion preferences. Use assets with known permission to publish; record their sources. Do not invent client testimonials, achievements or business facts.

Before expanding a design across all pages, show the first complete page at desktop and mobile widths. Describe the main design decisions and any unresolved content. When a browser tool is unavailable, report that visual verification is still pending.
File.agents/skills/clean-code/SKILL.md
---
name: clean-code
description: Implement or refactor website code into understandable components using the project's existing stack and conventions. Use for website implementation or maintainability work.
---

Read the relevant files and package scripts before choosing an implementation. Preserve working behaviour outside the requested change. Prefer the existing stack and dependencies when they meet the need.

Keep page content separate from repeated layout where that makes editing easier. Name components, variables and functions for their purpose. Use shared components for repeated navigation and page elements; avoid abstraction for a single trivial use.

Handle empty, invalid, loading and error states for interactions that need them. Use native browser controls and semantic HTML when they serve the interaction. Avoid fake form submission, simulated success messages and dead links.

Use type checking and the project's formatting or lint rules where configured. When adding a package, explain its purpose and any new maintenance or runtime requirements. Keep generated build output, dependencies and local environment files out of version control.

Run the existing checks relevant to the change, including a production build when output can change. Summarise changed behaviour, verification results and remaining limits. Explain the main files in plain language so a beginner can find and edit their content.
File.agents/skills/website-testing/SKILL.md
---
name: website-testing
description: Verify website changes through visitor journeys, appropriate automated tests and browser checks. Use when testing a website, investigating a failure or preparing a release.
---

Start from the brief and observable acceptance criteria. Inspect existing test and build commands; do not assume that a script exists. Choose checks based on the changed behaviour and the cost of failure.

Exercise the main visitor journey and affected links, navigation and forms. Include invalid input and relevant error states. For a contact form, verify actual delivery in the agreed test destination before reporting that it works. For an email link, explain that it opens the visitor's configured email app and does not send a message automatically.

Check narrow and wide screens in a browser. Include keyboard navigation, visible focus, accessible names, zoom and horizontal overflow. Automated accessibility results complement these manual checks and do not establish complete accessibility conformance.

Add automated tests for important behaviour or demonstrated regressions. Test observable outcomes and meaningful failure cases; avoid tests that merely repeat the implementation or match incidental wording. Use disposable test data and local fixtures. Never send real messages, charge payments or alter production data without the user's authorization.

Reproduce a failure, fix its cause and rerun affected checks. Report commands run, results, browser checks performed and anything not checked. A successful build shows that the site can be generated; verify visitor behaviour separately. Never report a check as passed when it was skipped or unavailable.
File.agents/skills/website-security/SKILL.md
---
name: website-security
description: Review a website's secrets, dependencies, inputs, permissions and deployment configuration, and repair scoped security findings. Use for requested security review or release preparation.
---

Identify the site's relevant surfaces: static pages, forms, backend routes, authentication, third-party scripts and stored data. Scope review to the actual architecture and authorized environment.

Keep credentials out of browser code, logs, prompts and Git. Distinguish build-time public configuration from server secrets. If a key was committed or exposed, stop using it, explain that deleting the file does not revoke the key, and have the owner revoke or rotate it before further use. Do not print the credential in your report.

Inspect applicable dependency advisories and assess whether the affected package and vulnerable behaviour are used. Repair within the project's compatible versions and rerun affected checks. Avoid automatic forced upgrades that may break the website.

For backend interactions, validate inputs on the server, encode output appropriately, and check authentication and authorization separately. Consider abuse controls for public forms or AI endpoints. An OpenAI API key belongs on the server; publishing a static site does not provide a secret server environment.

Check HTTPS and applicable security headers at the actual hosting layer. Collect only the data the feature needs, and explain its destination and retention. Do not claim legal compliance from a code scan.

Report each finding with its location, plausible impact, fix and verification. State review scope, tools used, unresolved findings and inaccessible surfaces. A clean scan is evidence about that scan's scope, not a guarantee that the website has no vulnerabilities. Do not scan third-party systems or deploy changes outside the authorized task.